Isolated range
Kali, Windows/AD and vulnerable Linux targets on a hard-coded lab network. Review the plan before anything runs.
SCOPE GUARD · PREVIEW → RUN ›_RANGE//ZERO
ISOLATED CYBER RANGE // BLUE TEAM LAB // LOCAL ONLY
Kali → Windows/AD and vulnerable Linux targets on an isolated 10.10.10.0/24. Curated scenarios, hard scope guard, real telemetry and reports that keep their receipts.
Six telemetry channels. A versioned rule pack. High signals sorted above noise. Every alert links back to a real event — not a decorative demo.
READ THE DETECTION PROOF →Kali, Windows/AD and vulnerable Linux targets on a hard-coded lab network. Review the plan before anything runs.
SCOPE GUARD · PREVIEW → RUNWindows Security/System/PowerShell, Kali journal and Suricata IDS in one evidence timeline. Versioned rules, real source health.
6 CHANNELS · 13 RULESEvidence-backed posture across app, privacy, host, network and lab. Reversible hardening previews and cited playbooks.
POSTURE HISTORY · PLAYBOOKSLive assets, NIST/CIS/ISO control mappings with honest gaps, detection evidence and JSON/Markdown export.
15 ASSETS · 10 CONTROLS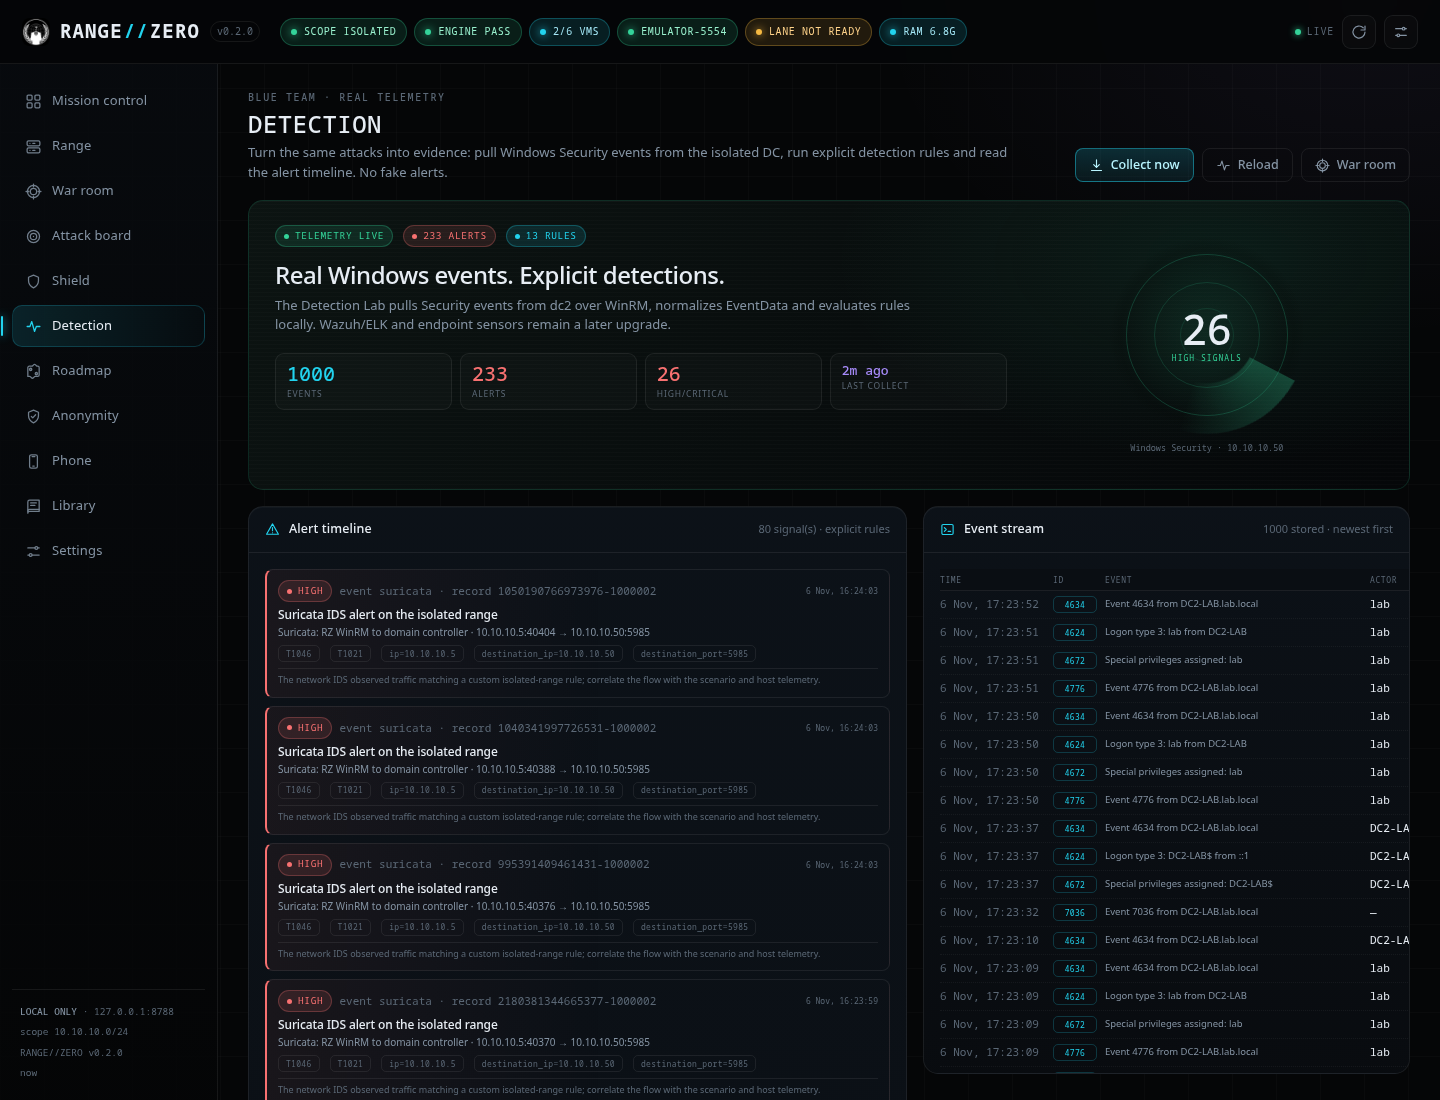
When the Kerberoast scenario runs, the Attack Board arc, the $krb5tgs$ evidence and the detection alert all come from the same isolated lab. The app shows the scope result and the raw transcript.
No anonymity guarantee. The lab is isolated and local; identity safety is a separate, verified lane.
Practice only against the isolated lab or systems with written authorization.
Detection Lab v5 is real but narrow. Wazuh/ELK and endpoint sensors are future work.
No accounts/MFA, multi-tenancy, SLA or external audit yet. This is a private pilot.
The public pilot is invite-only. The waitlist opens after the owner approves the privacy and pilot terms; no email is collected here. Practice stays in the isolated lab or systems with written authorization.