Isolated range
Kali, Windows/AD and vulnerable Linux targets on a hard-coded lab network. Review the plan before anything runs.
SCOPE GUARD · PREVIEW → RUN ›_RANGE//ZERO
ISOLATED CYBER RANGE // BLUE TEAM LAB // LOCAL ONLY
Kali → Windows/AD and vulnerable Linux targets on an isolated 10.10.10.0/24. Curated scenarios, hard scope guard, real telemetry and reports that keep their receipts.
Six telemetry channels. A versioned rule pack. High signals sorted above noise. Every alert links back to a real event — not a decorative demo.
READ THE DETECTION PROOF →Windows Security, System and PowerShell. Kali journal. Suricata IDS. A wired Sysmon channel. Detection Lab normalizes them, preserves source health and sorts high signals above noise.
High signals stay above older medium noise. Every alert points back to the source event and its rule.
Kali, Windows/AD and vulnerable Linux targets on a hard-coded lab network. Review the plan before anything runs.
SCOPE GUARD · PREVIEW → RUNWindows Security/System/PowerShell, Kali journal and Suricata IDS in one evidence timeline. Versioned rules, real source health.
6 CHANNELS · 13 RULESEvidence-backed posture across app, privacy, host, network and lab. Reversible hardening previews and cited playbooks.
POSTURE HISTORY · PLAYBOOKSLive assets, NIST/CIS/ISO control mappings with honest gaps, detection evidence and JSON/Markdown export.
15 ASSETS · 10 CONTROLSEach surface is measured, tested and limited. Open one and the evidence is already attached.
Eight curated scenarios against Kali, Windows/AD and vulnerable Linux targets. Preview every command, scope every IP, keep every transcript.
Windows Security/System/PowerShell, Kali journal and Suricata in one evidence timeline. High signals above noise, source health beside them.
Posture across app, privacy, host, network and lab. Reversible hardening previews, cited playbooks and a local trend — never a guarantee.
Live asset inventory, NIST/CIS/ISO mappings with honest gaps, detection evidence and JSON/Markdown export. Evidence, not a certification.
The port is not the point. The proof is. Every scenario is reviewed before it runs, verified while it runs and kept after the terminal closes.
Curated Kali → Windows/AD scenarios. Plan preview, scope guard, real SSH command, live output.
KALI → DC2 / WIN11Security, System, PowerShell, journal and Suricata evidence normalized into one alert timeline.
6 CHANNELS · 13 RULESTicket material, parsed ports, scope result and raw transcripts are attached to the run.
EVIDENCE, NOT A SCOREAssets, control mappings and detection evidence export locally as JSON and Markdown.
NIST · CIS · ISO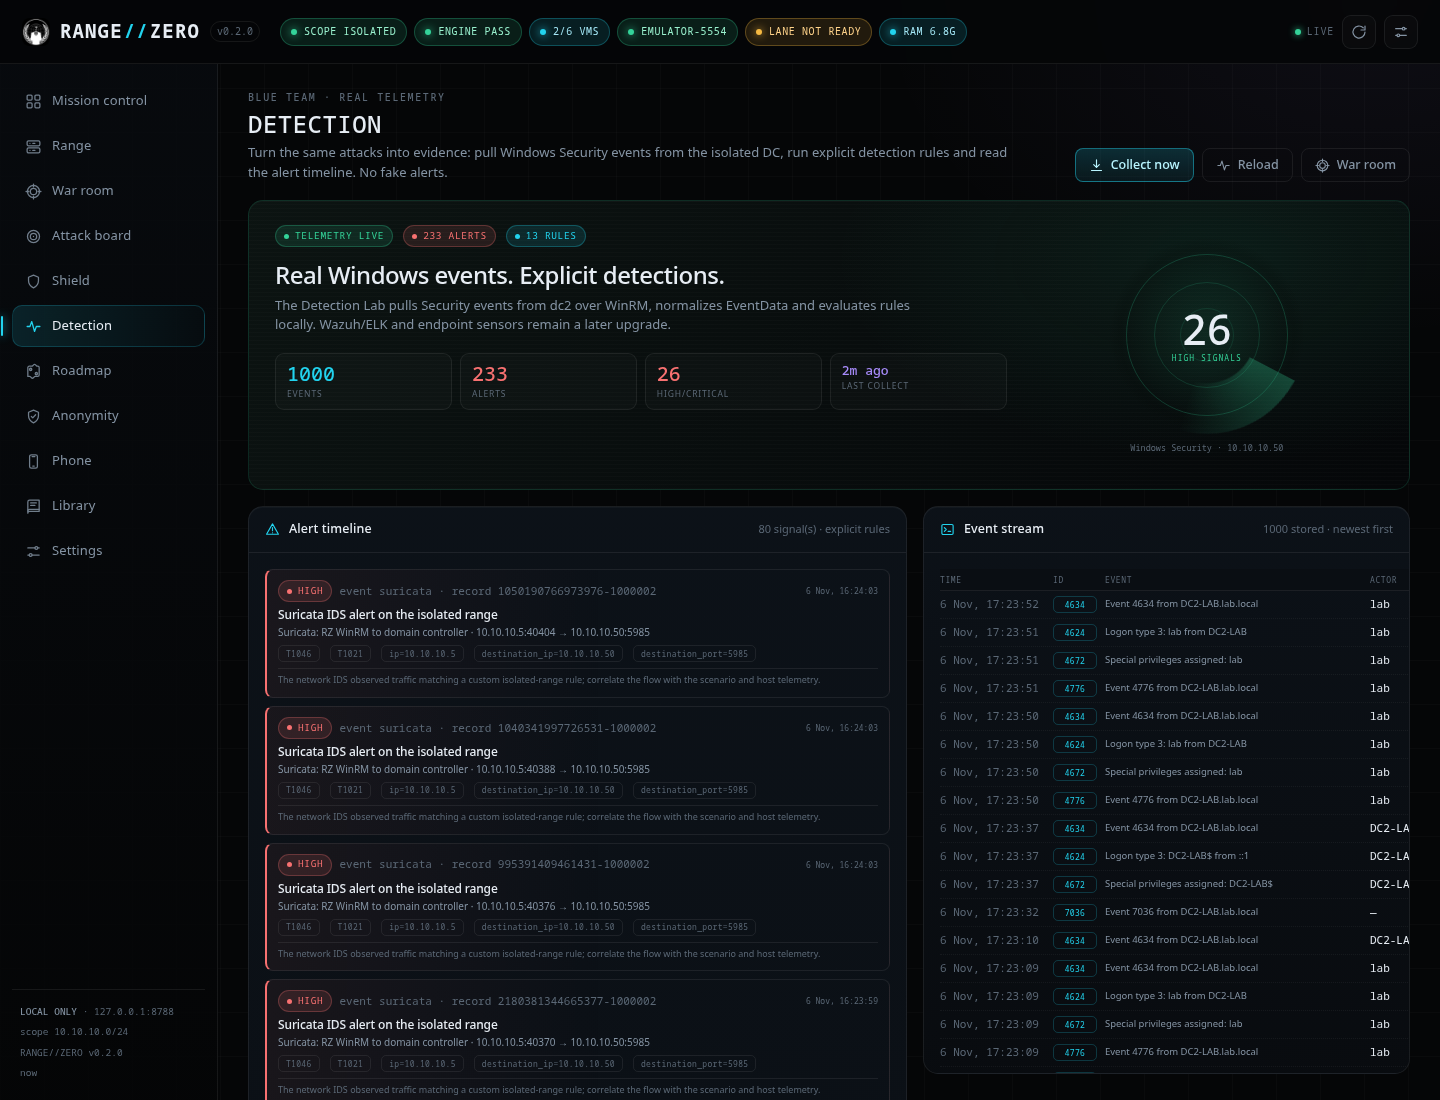
When the Kerberoast scenario runs, the Attack Board arc, the $krb5tgs$ evidence and the detection alert all come from the same isolated lab. The app shows the scope result and the raw transcript.
No anonymity guarantee. The lab is isolated and local; identity safety is a separate, verified lane.
Practice only against the isolated lab or systems with written authorization.
Detection Lab v5 is real but narrow. Wazuh/ELK and endpoint sensors are future work.
No accounts/MFA, multi-tenancy, SLA or external audit yet. This is a private pilot.
These are not slogans. They decide what ships, what is refused and what the evidence must show.
If it did not run in the lab and leave a trace, it does not go on the board.
The range stays on this machine. No telemetry, no third-party asset, no silent upload.
Every score names its scope, every rule names its gap. No untraceability promise.
Tests, manifests and transcripts outlive the person who ran the scenario.
Local services and real lab tooling. If it is not here, the page does not claim it.
The public pilot is invite-only. The waitlist opens after the owner approves the privacy and pilot terms; no email is collected here. Practice stays in the isolated lab or systems with written authorization.